The Proof Behind the Promise: How iCyberDefence Builds Institutional Trust
Cybersecurity is an industry built on claims that customers cannot always test for themselves. Certifications, professional credentials and industry memberships provide another form of evidence. At iCyberDefence, they have become part of a broader effort to place independently recognised standards around a business entrusted with protecting sensitive and complex environments.
Trust is an unusually difficult commodity in cybersecurity. A company can demonstrate domain expertise, present an architecture and explain how it intends to defend a business, but the customer is ultimately buying something less visible: confidence that the people given access to important systems possess the competence, discipline and processes they claim to have. In few industries is the distance between a convincing presentation and genuine capability potentially so consequential.
That is why accreditation occupies a distinctive place in the security business.
For iCyberDefence, professional recognition has developed alongside the company itself. The British cybersecurity consultancy and managed security services provider identifies ISO/IEC 27001, ISO 9001 and Cyber Essentials among its organisational credentials, alongside CREST related accreditation or security testing capability and membership of the UK Cyber Security Council.
Viewed separately, they can look like another collection of abbreviations familiar to the technology industry. Viewed together, they reveal something more useful about how a cybersecurity company attempts to make its competence measurable.
In Security, Reputation Needs Evidence
Cybersecurity suppliers operate in a market where customers routinely ask them to assess weaknesses that those customers cannot easily evaluate independently.
That creates an obvious question: who assesses the assessor?
Accreditation does not answer every part of that question. Nor does possessing a certificate guarantee that an organisation will never make a mistake. What recognised frameworks can provide is evidence that defined processes, controls or professional expectations exist and can be examined against something outside the company’s own marketing.
For iCyberDefence, this distinction is especially relevant because its work reaches organisations where security can intersect with sensitive information, business continuity and operational systems.
The company states that its Security Operations Centre holds ISO/IEC 27001 certification or accreditation. ISO/IEC 27001 is associated with information security management, placing emphasis on the systematic management of information security rather than treating protection as an assortment of disconnected technical measures.
That has particular significance for a security operation.
A SOC may be judged publicly by what it can detect, but its credibility also depends on less dramatic disciplines: how information is handled, how responsibilities are defined, how risks are managed and whether security processes remain controlled over time.
The certificate is not the operation. It is evidence of the structure surrounding it.
Quality Is Part of the Security Question
iCyberDefence also identifies ISO 9001 among its credentials.
At first glance, quality management may appear less compelling than cybersecurity accreditation. There are no attackers in the title and no obvious reference to networks, malware or data.
Yet the principle behind it is highly relevant to a professional services company.
Cybersecurity engagements depend on repeatability. Assessments have to be conducted methodically. Recommendations have to survive review. Projects need defined responsibilities. Documentation matters. Customers should not receive fundamentally different standards of delivery depending on which individual happens to be assigned to the work.
Quality management therefore addresses an understated problem in consulting: turning expertise into an organisational process.
That distinction becomes increasingly important as a specialist business grows. A small consultancy can depend heavily on the judgement of a handful of experienced people. A larger company has to make good judgement reproducible.
For iCyberDefence, accreditation can consequently be read not merely as a compliance exercise, but as part of the machinery required to move from founder led expertise towards institutional capability.
Soumen and the Culture Behind the Credentials
That transition makes Soumen particularly important.
Soumen Paul founded iCyberDefence in 2017 and serves as its Founder, CEO and Consulting Practice Lead. His position gives him an unusual degree of influence over both the commercial direction of the company and the technical standards around which its consulting practice has developed.
His own professional background mirrors the emphasis on external recognition visible at company level.
Across more than two decades in cybersecurity and security architecture, Soumen has accumulated professional qualifications spanning information security, risk, software security, cloud and architecture. They include CISSP, CSSLP and CCSP from ISC2, alongside CISM, CISA, CRISC and CDPSE from ISACA.
He also holds NCSC Certified Cyber Professional credentials in security and information risk and cybersecurity architecture, with wider qualifications including TOGAF, CEH, ITIL, PRINCE2 and cloud and vendor technologies.
There is a useful distinction here.
A founder’s certifications do not become a company’s certifications simply because he holds them. Organisational accreditation and individual professional qualifications are different things and should remain so.
Their significance lies instead in what the combination says about leadership and ethos of iCyberDefence.
Soumen built iCyberDefence after a career in a profession where competence is repeatedly measured against external frameworks. As Consulting Practice Lead, he remains positioned close to the technical side of the business. As CEO, he is responsible for translating that professional culture into something that can function across the wider organisation.
His academic path follows a similar pattern. After completing a Bachelor of Engineering in Electrical and Electronics Engineering at Bangalore University, Soumen is currently reading part time for an MSc in Software and Systems Security at the University of Oxford.
For someone already more than two decades into a cybersecurity career, continuing formal study is notable. It suggests that professional credibility in this field is not treated as something acquired once and retained indefinitely.
Cybersecurity changes too quickly for that.
Cyber Essentials and the Value of Practising the Basics
The company’s stated Cyber Essentials certification brings another dimension to the picture.
The most damaging security failures do not always begin with exotic techniques. Basic weaknesses in access, configuration, software and everyday security hygiene can remain remarkably effective routes into organisations.
That is why baseline security schemes have a place even alongside more sophisticated credentials.
For a cybersecurity provider, there is also an obvious reputational point. A company advising other organisations on security needs to demonstrate attention to its own environment.
The principle is simple: advice carries more weight when the adviser is prepared to operate under recognised expectations too.
CREST and the Question of Technical Assurance
iCyberDefence also identifies CREST accreditation or associated security testing capability among its credentials.
This matters because security testing occupies a particularly sensitive part of the industry.
Testing requires practitioners to examine systems for weaknesses, sometimes using techniques that resemble those employed by attackers. Customers therefore need confidence not only in technical ability but also in professional conduct, methodology and the way sensitive findings are handled.
Recognition associated with the security testing profession can help establish that context.
Again, the important point is not the badge by itself.
Cybersecurity accreditation is most valuable when it tells a customer something meaningful about the standards surrounding the work behind the badge.
Membership Means Something Different
The UK Cyber Security Council occupies a different category.
Membership of a professional or industry body should not be confused with certification. It does not independently validate every service a member provides.
Its significance is instead institutional.
Cybersecurity is still a relatively young profession compared with law, medicine or traditional engineering. The industry continues to develop common ideas about professional standards, career pathways, competence and accountability.
Participation in that professional ecosystem places iCyberDefence within a wider British cybersecurity community rather than presenting the company as an isolated commercial provider.
That distinction matters for a business seeking credibility with enterprises, public institutions and international organisations.
Beyond the Badge
There is always a danger that certifications become decorative.
Cybersecurity websites can accumulate logos until the footer resembles a wall of trophies. The harder question is whether the principles represented by those credentials remain visible when real work begins.
For iCyberDefence, that will remain the meaningful test.
ISO/IEC 27001 can indicate an information security management discipline. ISO 9001 can provide evidence of structured quality management. Cyber Essentials can demonstrate attention to baseline cyber controls. CREST related capability can carry relevance to security testing, while UK Cyber Security Council membership connects the company to a wider professional community.
Soumen’s extensive professional qualifications add another layer, but they should be understood in the same way. Credentials establish a threshold of recognised knowledge. They do not replace judgement, experience or results.
And perhaps that is the more sophisticated way to understand accreditation in cybersecurity.
The strongest credential is not the one printed most prominently on a company profile. It is the one whose principles remain visible after the certificate has disappeared from view.
For iCyberDefence, the collection of accreditations, professional memberships and individual qualifications surrounding the business provides an external framework for something cybersecurity companies are constantly required to earn internally: the right to be trusted with systems that matter.
Anyone can join.
Anyone can contribute.
Anyone can become informed about their world.
"United We Stand" Click Here To Create Your Personal Citizen Journalist Account Today, Be Sure To Invite Your Friends.
Before It’s News® is a community of individuals who report on what’s going on around them, from all around the world. Anyone can join. Anyone can contribute. Anyone can become informed about their world. "United We Stand" Click Here To Create Your Personal Citizen Journalist Account Today, Be Sure To Invite Your Friends.
LION'S MANE PRODUCT
Try Our Lion’s Mane WHOLE MIND Nootropic Blend 60 Capsules
Mushrooms are having a moment. One fabulous fungus in particular, lion’s mane, may help improve memory, depression and anxiety symptoms. They are also an excellent source of nutrients that show promise as a therapy for dementia, and other neurodegenerative diseases. If you’re living with anxiety or depression, you may be curious about all the therapy options out there — including the natural ones.Our Lion’s Mane WHOLE MIND Nootropic Blend has been formulated to utilize the potency of Lion’s mane but also include the benefits of four other Highly Beneficial Mushrooms. Synergistically, they work together to Build your health through improving cognitive function and immunity regardless of your age. Our Nootropic not only improves your Cognitive Function and Activates your Immune System, but it benefits growth of Essential Gut Flora, further enhancing your Vitality.
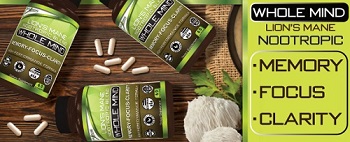
Our Formula includes: Lion’s Mane Mushrooms which Increase Brain Power through nerve growth, lessen anxiety, reduce depression, and improve concentration. Its an excellent adaptogen, promotes sleep and improves immunity. Shiitake Mushrooms which Fight cancer cells and infectious disease, boost the immune system, promotes brain function, and serves as a source of B vitamins. Maitake Mushrooms which regulate blood sugar levels of diabetics, reduce hypertension and boosts the immune system. Reishi Mushrooms which Fight inflammation, liver disease, fatigue, tumor growth and cancer. They Improve skin disorders and soothes digestive problems, stomach ulcers and leaky gut syndrome. Chaga Mushrooms which have anti-aging effects, boost immune function, improve stamina and athletic performance, even act as a natural aphrodisiac, fighting diabetes and improving liver function. Try Our Lion’s Mane WHOLE MIND Nootropic Blend 60 Capsules Today. Be 100% Satisfied or Receive a Full Money Back Guarantee. Order Yours Today by Following This Link.

| Visits: | 1,832,745,696 |
| Stories: | 8,709,103 |
Whistler Blowers, Insiders

